Manages data for an authenticated session. More...
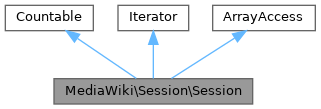
Inherits Countable, Iterator, and ArrayAccess.
Public Member Functions | |
| __construct (SessionBackend $backend, $index, LoggerInterface $logger) | |
| __destruct () | |
| allowSecuritySensitiveOperationIfCannotReauthenticate () | |
| Whether security-sensitive operations should be allowed at all. | |
| canSetUser () | |
| Indicate whether the session user info can be changed. | |
| clear () | |
| Delete all session data and clear the user (if possible) | |
| delaySave () | |
| Delay automatic saving while multiple updates are being made. | |
| exists ( $key) | |
| Test if a value exists in the session. | |
| get ( $key, $default=null) | |
| Fetch a value from the session. | |
| getAllowedUserRights () | |
| getId () | |
| Returns the session ID. | |
| getLoggedOutTimestamp () | |
| Fetch the "logged out" timestamp. | |
| getProvider () | |
| Fetch the SessionProvider for this session. | |
| getProviderMetadata () | |
| Fetch provider metadata. | |
| getRequest () | |
| Return the request associated with this session. | |
| getRestrictions () | |
| getSecret ( $key, $default=null) | |
| Fetch a value from the session that was set with self::setSecret() | |
| getSessionId () | |
| Returns the SessionId object. | |
| getToken ( $salt='', $key='default') | |
| Fetch a CSRF token from the session. | |
| getUser () | |
| Return the authenticated user for this session. | |
| hasToken (string $key='default') | |
| Check if a CSRF token is set for the session. | |
| isPersistent () | |
| Indicate whether this session is persisted across requests. | |
| persist () | |
| Make this session persisted across requests. | |
| remove ( $key) | |
| renew () | |
| resetAllTokens () | |
| Remove all CSRF tokens from the session. | |
| resetId () | |
| Changes the session ID. | |
| resetToken ( $key='default') | |
| Remove a CSRF token from the session. | |
| save () | |
| This will update the backend data and might re-persist the session if needed. | |
| sessionWithRequest (WebRequest $request) | |
| Fetch a copy of this session attached to an alternative WebRequest. | |
| set ( $key, $value) | |
| setForceHTTPS ( $force) | |
| Set the value of the forceHTTPS cookie. | |
| setLoggedOutTimestamp ( $ts) | |
| setRememberUser ( $remember) | |
| Set whether the user should be remembered independently of the session ID. | |
| setSecret ( $key, $value) | |
| Set a value in the session, encrypted. | |
| setUser ( $user) | |
| Set a new user for this session. | |
| shouldForceHTTPS () | |
| Get the expected value of the forceHTTPS cookie. | |
| shouldRememberUser () | |
| Indicate whether the user should be remembered independently of the session ID. | |
| suggestLoginUsername () | |
| unpersist () | |
| Make this session not be persisted across requests. | |
Interface methods | |
| count () | |
| current () | |
| key () | |
| next () | |
| rewind () | |
| valid () | |
| offsetExists ( $offset) | |
| & | offsetGet ( $offset) |
| offsetSet ( $offset, $value) | |
| offsetUnset ( $offset) | |
Detailed Description
Manages data for an authenticated session.
A Session represents the fact that the current HTTP request is part of a session. There are two broad types of Sessions, based on whether they return true or false from self::canSetUser():
- When true (mutable), the Session identifies multiple requests as part of a session generically, with no tie to a particular user.
- When false (immutable), the Session identifies multiple requests as part of a session by identifying and authenticating the request itself as belonging to a particular user.
The Session object also serves as a replacement for PHP's $_SESSION, managing access to per-session data.
- Since
- 1.27
Definition at line 38 of file Session.php.
Constructor & Destructor Documentation
◆ __construct()
| MediaWiki\Session\Session::__construct | ( | SessionBackend | $backend, |
| $index, | |||
| LoggerInterface | $logger ) |
- Parameters
-
SessionBackend $backend int $index LoggerInterface $logger
Definition at line 58 of file Session.php.
◆ __destruct()
| MediaWiki\Session\Session::__destruct | ( | ) |
Definition at line 64 of file Session.php.
Member Function Documentation
◆ allowSecuritySensitiveOperationIfCannotReauthenticate()
| MediaWiki\Session\Session::allowSecuritySensitiveOperationIfCannotReauthenticate | ( | ) |
Whether security-sensitive operations should be allowed at all.
- See also
- SessionProvider::allowSecuritySensitiveOperationIfCannotReauthenticate()
- Returns
- bool
Definition at line 198 of file Session.php.
◆ canSetUser()
| MediaWiki\Session\Session::canSetUser | ( | ) |
Indicate whether the session user info can be changed.
- Returns
- bool
Definition at line 188 of file Session.php.
◆ clear()
| MediaWiki\Session\Session::clear | ( | ) |
Delete all session data and clear the user (if possible)
Definition at line 277 of file Session.php.
◆ count()
| MediaWiki\Session\Session::count | ( | ) |
Definition at line 599 of file Session.php.
◆ current()
| MediaWiki\Session\Session::current | ( | ) |
Definition at line 606 of file Session.php.
◆ delaySave()
| MediaWiki\Session\Session::delaySave | ( | ) |
Delay automatic saving while multiple updates are being made.
Calls to save() or clear() will not be delayed.
- Returns
- \Wikimedia\ScopedCallback When this goes out of scope, a save will be triggered
Definition at line 581 of file Session.php.
◆ exists()
| MediaWiki\Session\Session::exists | ( | $key | ) |
Test if a value exists in the session.
- Note
- Unlike isset(), null values are considered to exist.
- Parameters
-
string | int $key
- Returns
- bool
Definition at line 330 of file Session.php.
◆ get()
| MediaWiki\Session\Session::get | ( | $key, | |
| $default = null ) |
Fetch a value from the session.
- Parameters
-
string | int $key mixed | null $default Returned if $this->exists( $key )would be false
- Returns
- mixed
Definition at line 317 of file Session.php.
Referenced by MediaWiki\User\TempUser\TempUserCreator\acquireAndStashName().
◆ getAllowedUserRights()
| MediaWiki\Session\Session::getAllowedUserRights | ( | ) |
- See also
- SessionProvider::getAllowedUserRights
- Returns
- null|string[] Allowed user rights, or null to allow all.
Definition at line 172 of file Session.php.
◆ getId()
| MediaWiki\Session\Session::getId | ( | ) |
◆ getLoggedOutTimestamp()
| MediaWiki\Session\Session::getLoggedOutTimestamp | ( | ) |
◆ getProvider()
| MediaWiki\Session\Session::getProvider | ( | ) |
Fetch the SessionProvider for this session.
- Returns
- SessionProviderInterface
Definition at line 97 of file Session.php.
◆ getProviderMetadata()
| MediaWiki\Session\Session::getProviderMetadata | ( | ) |
Fetch provider metadata.
- Note
- For use by SessionProvider subclasses only
- Returns
- mixed
Definition at line 270 of file Session.php.
◆ getRequest()
| MediaWiki\Session\Session::getRequest | ( | ) |
Return the request associated with this session.
- Returns
- WebRequest
Definition at line 157 of file Session.php.
Referenced by MediaWiki\User\TempUser\TempUserCreator\acquireAndStashName().
◆ getRestrictions()
| MediaWiki\Session\Session::getRestrictions | ( | ) |
- See also
- SessionProvider::getRestrictions
- Returns
- MWRestrictions|null
Definition at line 180 of file Session.php.
◆ getSecret()
| MediaWiki\Session\Session::getSecret | ( | $key, | |
| $default = null ) |
Fetch a value from the session that was set with self::setSecret()
- Parameters
-
string | int $key mixed | null $default Returned if $this->exists( $key ) would be false or decryption fails
- Returns
- mixed
Definition at line 524 of file Session.php.
◆ getSessionId()
| MediaWiki\Session\Session::getSessionId | ( | ) |
Returns the SessionId object.
- Access: internal
- For internal use by WebRequest
- Returns
- SessionId
Definition at line 81 of file Session.php.
Referenced by MediaWiki\Request\FauxRequest\__construct().
◆ getToken()
| MediaWiki\Session\Session::getToken | ( | $salt = '', | |
| $key = 'default' ) |
Fetch a CSRF token from the session.
Note that this does not persist the session, which you'll probably want to do if you want the token to actually be useful.
- Parameters
-
string | string[] $salt Token salt string $key Token key
- Returns
- Token
Definition at line 383 of file Session.php.
Referenced by MediaWiki\Auth\ElevatedSecurityAuthenticationRequest\create().
◆ getUser()
| MediaWiki\Session\Session::getUser | ( | ) |
Return the authenticated user for this session.
Definition at line 164 of file Session.php.
Referenced by MediaWiki\Auth\ElevatedSecurityAuthenticationRequest\create().
◆ hasToken()
| MediaWiki\Session\Session::hasToken | ( | string | $key = 'default' | ) |
Check if a CSRF token is set for the session.
- Since
- 1.37
- Parameters
-
string $key Token key
- Returns
- bool
Definition at line 365 of file Session.php.
◆ isPersistent()
| MediaWiki\Session\Session::isPersistent | ( | ) |
Indicate whether this session is persisted across requests.
For example, if cookies are set.
- Returns
- bool
Definition at line 108 of file Session.php.
◆ key()
| MediaWiki\Session\Session::key | ( | ) |
Definition at line 613 of file Session.php.
◆ next()
| MediaWiki\Session\Session::next | ( | ) |
Definition at line 619 of file Session.php.
◆ offsetExists()
| MediaWiki\Session\Session::offsetExists | ( | $offset | ) |
- Note
- Despite the name, this seems to be intended to implement isset() rather than array_key_exists(). So do that.
Definition at line 641 of file Session.php.
◆ offsetGet()
| & MediaWiki\Session\Session::offsetGet | ( | $offset | ) |
- Note
- This supports indirect modifications but can't mark the session dirty when those happen. SessionBackend::save() checks the hash of the data to detect such changes.
- Accessing a nonexistent key via this mechanism causes that key to be created with a null value, and does not raise a PHP warning.
Definition at line 655 of file Session.php.
◆ offsetSet()
| MediaWiki\Session\Session::offsetSet | ( | $offset, | |
| $value ) |
Definition at line 665 of file Session.php.
◆ offsetUnset()
| MediaWiki\Session\Session::offsetUnset | ( | $offset | ) |
Definition at line 670 of file Session.php.
◆ persist()
| MediaWiki\Session\Session::persist | ( | ) |
Make this session persisted across requests.
If the session is already persistent, equivalent to calling $this->renew().
Definition at line 118 of file Session.php.
Referenced by MediaWiki\Auth\ElevatedSecurityAuthenticationRequest\create().
◆ remove()
| MediaWiki\Session\Session::remove | ( | $key | ) |
- Parameters
-
string | int $key
Definition at line 350 of file Session.php.
◆ renew()
| MediaWiki\Session\Session::renew | ( | ) |
- See also
- SessionBackend::renew
Definition at line 292 of file Session.php.
◆ resetAllTokens()
| MediaWiki\Session\Session::resetAllTokens | ( | ) |
Remove all CSRF tokens from the session.
Definition at line 423 of file Session.php.
◆ resetId()
| MediaWiki\Session\Session::resetId | ( | ) |
Changes the session ID.
- Returns
- string New ID (might be the same as the old)
Definition at line 89 of file Session.php.
◆ resetToken()
| MediaWiki\Session\Session::resetToken | ( | $key = 'default' | ) |
Remove a CSRF token from the session.
The next call to self::getToken() with $key will generate a new secret.
- Parameters
-
string $key Token key
Definition at line 411 of file Session.php.
◆ rewind()
| MediaWiki\Session\Session::rewind | ( | ) |
Definition at line 625 of file Session.php.
◆ save()
| MediaWiki\Session\Session::save | ( | ) |
This will update the backend data and might re-persist the session if needed.
Definition at line 589 of file Session.php.
Referenced by MediaWiki\User\TempUser\TempUserCreator\acquireAndStashName().
◆ sessionWithRequest()
| MediaWiki\Session\Session::sessionWithRequest | ( | WebRequest | $request | ) |
Fetch a copy of this session attached to an alternative WebRequest.
Actions on the copy will affect this session too, and vice versa.
- Parameters
-
WebRequest $request Any existing session associated with this WebRequest object will be overwritten.
- Returns
- self
Definition at line 305 of file Session.php.
References $request.
◆ set()
| MediaWiki\Session\Session::set | ( | $key, | |
| $value ) |
- Parameters
-
string | int $key mixed $value
Definition at line 339 of file Session.php.
Referenced by MediaWiki\User\TempUser\TempUserCreator\acquireAndStashName().
◆ setForceHTTPS()
| MediaWiki\Session\Session::setForceHTTPS | ( | $force | ) |
Set the value of the forceHTTPS cookie.
This reflects whether session cookies were sent with the Secure attribute. If $wgForceHTTPS is true, the forceHTTPS cookie is not sent, and this value is ignored.
- Parameters
-
bool $force
Definition at line 243 of file Session.php.
◆ setLoggedOutTimestamp()
| MediaWiki\Session\Session::setLoggedOutTimestamp | ( | $ts | ) |
- Parameters
-
int $ts
Definition at line 259 of file Session.php.
◆ setRememberUser()
| MediaWiki\Session\Session::setRememberUser | ( | $remember | ) |
Set whether the user should be remembered independently of the session ID.
- Parameters
-
bool $remember
Definition at line 148 of file Session.php.
◆ setSecret()
| MediaWiki\Session\Session::setSecret | ( | $key, | |
| $value ) |
Set a value in the session, encrypted.
This relies on the secrecy of $wgSecretKey (by default), or $wgSessionSecret.
- Parameters
-
string | int $key mixed $value
Definition at line 488 of file Session.php.
◆ setUser()
| MediaWiki\Session\Session::setUser | ( | $user | ) |
Set a new user for this session.
- Note
- This should only be called when the user has been authenticated
TODO: Consider changing this to a "UserIdentity" instead.
- Parameters
-
User $user User to set on the session.
Definition at line 211 of file Session.php.
◆ shouldForceHTTPS()
| MediaWiki\Session\Session::shouldForceHTTPS | ( | ) |
Get the expected value of the forceHTTPS cookie.
This reflects whether session cookies were sent with the Secure attribute. If $wgForceHTTPS is true, the 'forceHTTPS' cookie is not sent and this value is ignored.
- Returns
- bool
Definition at line 231 of file Session.php.
◆ shouldRememberUser()
| MediaWiki\Session\Session::shouldRememberUser | ( | ) |
Indicate whether the user should be remembered independently of the session ID.
- Returns
- bool
Definition at line 139 of file Session.php.
◆ suggestLoginUsername()
| MediaWiki\Session\Session::suggestLoginUsername | ( | ) |
- See also
- SessionProvider::suggestLoginUsername
- Returns
- string|null
Definition at line 219 of file Session.php.
◆ unpersist()
| MediaWiki\Session\Session::unpersist | ( | ) |
Make this session not be persisted across requests.
This will remove persistence information (e.g. delete cookies) from the associated WebRequest(s), and delete session data in the backend. The session data will still be available via get() until the end of the request.
Definition at line 130 of file Session.php.
◆ valid()
| MediaWiki\Session\Session::valid | ( | ) |
Definition at line 631 of file Session.php.
The documentation for this class was generated from the following file:
- includes/Session/Session.php
