This serves as the entry point to the MediaWiki session handling system. More...
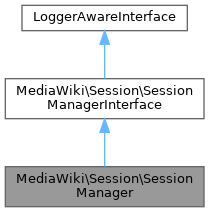
Inherits MediaWiki\Session\SessionManagerInterface.
Public Member Functions | ||||||||||
| __construct (Config $config, LoggerInterface $logger, CentralIdLookup $centralIdLookup, HookContainer $hookContainer, ObjectFactory $objectFactory, ProxyLookup $proxyLookup, UrlUtils $urlUtils, UserNameUtils $userNameUtils, SessionStore $sessionStore) | ||||||||||
| getAllOpenApiSecuritySchemes () | ||||||||||
| Gathers the OpenAPI security schemes from all registered SessionProviders. | ||||||||||
| getEmptySession (?WebRequest $request=null) | ||||||||||
Create a new, empty session.The first provider configured that is able to provide an empty session will be used.
| ||||||||||
| getJwtData (UserIdentity $user) | ||||||||||
| Return a set of key-value pairs applicable for use as claims in a JSON Web Token. | ||||||||||
| getSessionById ( $id, $create=false, ?WebRequest $request=null) | ||||||||||
Fetch a session by ID.
| ||||||||||
| getSessionForRequest (WebRequest $request) | ||||||||||
Fetch the session for a request (or a new empty session if none is attached to it)
\OverflowException if there are multiple sessions tied for top priority in the request. Exception has a property "sessionInfos" holding the SessionInfo objects for the sessions involved. | ||||||||||
| getVaryCookies () | ||||||||||
Return the list of cookies that need varying on.
| ||||||||||
| getVaryHeaders () | ||||||||||
| invalidateSessionsForUser (User $user) | ||||||||||
| Invalidate sessions for a user. | ||||||||||
| setHookContainer (HookContainer $hookContainer) | ||||||||||
| setLogger (LoggerInterface $logger) | ||||||||||
| validateJwtSubject (array $jwtData, UserIdentity $user) | ||||||||||
| Partially validate JWT data that's presumed to be generated by getJwtData(). | ||||||||||
Static Public Member Functions | |
| static | getGlobalSession () |
| static | validateSessionId ( $id) |
| Validate a session ID. | |
Internal methods | |
| preventSessionsForUser ( $username) | |
| Prevent future sessions for the user. | |
| isUserSessionPrevented ( $username) | |
| Test if a user is prevented. | |
| getProvider ( $name) | |
| Get a session provider by name. | |
| shutdown () | |
| Save all active sessions on shutdown. | |
| getSessionFromInfo (SessionInfo $info, WebRequest $request) | |
| Create a Session corresponding to the passed SessionInfo. | |
| changeBackendId (SessionBackend $backend) | |
| Change a SessionBackend's ID. | |
| generateSessionId () | |
| Generate a new random session ID. | |
| logPotentialSessionLeakage (?Session $session=null) | |
| Write debug logs if the current request may have experienced session leak bug. | |
| getProviders () | |
| Get the available SessionProviders. | |
Detailed Description
This serves as the entry point to the MediaWiki session handling system.
Most methods here are for internal use by session handling code. Other callers should only use the methods of SessionManagerInterface; the rest of the functionality is exposed via MediaWiki\Session\Session methods, which can be accessed from WebRequest::getSession().
To provide custom session handling, implement a MediaWiki\Session\SessionProvider.
See SessionStore Storage expectations.
- Since
- 1.27
Definition at line 54 of file SessionManager.php.
Constructor & Destructor Documentation
◆ __construct()
| MediaWiki\Session\SessionManager::__construct | ( | Config | $config, |
| LoggerInterface | $logger, | ||
| CentralIdLookup | $centralIdLookup, | ||
| HookContainer | $hookContainer, | ||
| ObjectFactory | $objectFactory, | ||
| ProxyLookup | $proxyLookup, | ||
| UrlUtils | $urlUtils, | ||
| UserNameUtils | $userNameUtils, | ||
| SessionStore | $sessionStore ) |
Definition at line 104 of file SessionManager.php.
Member Function Documentation
◆ changeBackendId()
| MediaWiki\Session\SessionManager::changeBackendId | ( | SessionBackend | $backend | ) |
Change a SessionBackend's ID.
- Access: internal
- For use from \MediaWiki\Session\SessionBackend only
- Parameters
-
SessionBackend $backend
Definition at line 1025 of file SessionManager.php.
References MediaWiki\Session\SessionBackend\getSessionId().
◆ generateSessionId()
| MediaWiki\Session\SessionManager::generateSessionId | ( | ) |
◆ getAllOpenApiSecuritySchemes()
| MediaWiki\Session\SessionManager::getAllOpenApiSecuritySchemes | ( | ) |
Gathers the OpenAPI security schemes from all registered SessionProviders.
Iterates through all active session providers (from both Core and Extensions) and collects their OpenAPI security scheme definitions. Each scheme key is auto-generated from the provider's name (its string representation, which defaults to the fully qualified PHP class name, with backslashes replaced by hyphens), followed by a hyphen and the scheme-specific suffix returned by the provider. Using the provider's name keeps keys unique even if two providers share the same class, matching the uniqueness guarantee SessionManager enforces on provider names.
Example: CookieSessionProvider returning [ 'Session' => [...] ] produces the key "MediaWiki-Session-CookieSessionProvider-Session" in the returned array.
- Since
- 1.47
- Returns
- array<string, array> An associative array of security schemes for the OpenAPI components.securitySchemes object.
Implements MediaWiki\Session\SessionManagerInterface.
Definition at line 352 of file SessionManager.php.
◆ getEmptySession()
| MediaWiki\Session\SessionManager::getEmptySession | ( | ?WebRequest | $request = null | ) |
Create a new, empty session.The first provider configured that is able to provide an empty session will be used.
- Parameters
-
WebRequest | null $request Corresponding request. Any existing session associated with this WebRequest object will be overwritten.
- Returns
- Session
Implements MediaWiki\Session\SessionManagerInterface.
Definition at line 194 of file SessionManager.php.
References $request.
◆ getGlobalSession()
|
static |
- Deprecated
- since 1.45 Use RequestContext::getMain()->getRequest()->getSession() instead
Definition at line 100 of file SessionManager.php.
◆ getJwtData()
| MediaWiki\Session\SessionManager::getJwtData | ( | UserIdentity | $user | ) |
Return a set of key-value pairs applicable for use as claims in a JSON Web Token.
This can be used to standardize some session credentials as JWTs. It is up to individual session providers whether and how to use JWTs, but if they use them, they should make use of this mechanism so that infrastructure outside MediaWiki that makes use of such JWTs can be standardized.
Providers which call this method are free to extend or replace the values whenever that makes sense, but are encouraged to add at least the following fields:
- exp: hard expiry (as a UNIX timestamp), requests using this session token should be rejected after this point in time.
- sxp: soft expiry (if different from hard expiry), the session token should be ignored and the session treated as anonymous after this point.
- Parameters
-
UserIdentity $user The user who is the subject of the claim.
- Returns
- array A set of JWT claims (key-value pairs) as a JSON array.
- Since
- 1.45
- See also
- GetSessionJwtDataHook
- self::validateJwtSubject()
- JwtCodec::create()
Implements MediaWiki\Session\SessionManagerInterface.
Definition at line 393 of file SessionManager.php.
◆ getProvider()
| MediaWiki\Session\SessionManager::getProvider | ( | $name | ) |
Get a session provider by name.
Generally, this will only be used by internal implementation of some special session-providing mechanism. General purpose code, if it needs to access a SessionProvider at all, will use Session::getProvider().
- Parameters
-
string $name
- Returns
- SessionProvider|null
Definition at line 573 of file SessionManager.php.
◆ getProviders()
|
protected |
Get the available SessionProviders.
- Returns
- SessionProvider[]
Definition at line 538 of file SessionManager.php.
◆ getSessionById()
| MediaWiki\Session\SessionManager::getSessionById | ( | $id, | |
| $create = false, | |||
| ?WebRequest | $request = null ) |
Fetch a session by ID.
- Parameters
-
string $id bool $create If no session exists for $id, try to create a new one. May still return null if a session for $id exists but cannot be loaded. WebRequest | null $request Corresponding request. Any existing session associated with this WebRequest object will be overwritten.
- Returns
- Session|null
Implements MediaWiki\Session\SessionManagerInterface.
Definition at line 153 of file SessionManager.php.
References $request.
◆ getSessionForRequest()
| MediaWiki\Session\SessionManager::getSessionForRequest | ( | WebRequest | $request | ) |
Fetch the session for a request (or a new empty session if none is attached to it)
- Access: internal
- For WebRequest only. Use $request->getSession() instead. It's more efficient and doesn't break FauxRequests or sessions that were changed by $this->getSessionById() or $this->getEmptySession().
- Parameters
-
WebRequest $request Any existing associated session will be reset to the session corresponding to the data in the request itself.
- Returns
- Session
- Exceptions
-
\OverflowException if there are multiple sessions tied for top priority in the request. Exception has a property "sessionInfos" holding the SessionInfo objects for the sessions involved.
Implements MediaWiki\Session\SessionManagerInterface.
Definition at line 140 of file SessionManager.php.
References $request.
◆ getSessionFromInfo()
| MediaWiki\Session\SessionManager::getSessionFromInfo | ( | SessionInfo | $info, |
| WebRequest | $request ) |
Create a Session corresponding to the passed SessionInfo.
- Access: internal
- For use by a SessionProvider that needs to specially create its own Session. Most session providers won't need this.
- Parameters
-
SessionInfo $info WebRequest $request
- Returns
- Session
Definition at line 964 of file SessionManager.php.
References $request, MediaWiki\Session\SessionInfo\getId(), MediaWiki\Session\SessionInfo\isIdSafe(), MW_ENTRY_POINT, MW_NO_SESSION, MediaWiki\Session\SessionInfo\needsRefresh(), MediaWiki\Session\SessionInfo\wasPersisted(), and MediaWiki\Session\SessionInfo\wasRemembered().
◆ getVaryCookies()
| MediaWiki\Session\SessionManager::getVaryCookies | ( | ) |
Return the list of cookies that need varying on.
- Returns
- string[]
Implements MediaWiki\Session\SessionManagerInterface.
Definition at line 318 of file SessionManager.php.
References MW_NO_SESSION.
◆ getVaryHeaders()
| MediaWiki\Session\SessionManager::getVaryHeaders | ( | ) |
- Returns
- array<string,null>
Implements MediaWiki\Session\SessionManagerInterface.
Definition at line 299 of file SessionManager.php.
References MW_NO_SESSION.
◆ invalidateSessionsForUser()
| MediaWiki\Session\SessionManager::invalidateSessionsForUser | ( | User | $user | ) |
Invalidate sessions for a user.
After calling this, existing sessions should be invalid. For mutable session providers, this generally means the user has to log in again; for immutable providers, it generally means the loss of session data.
Implements MediaWiki\Session\SessionManagerInterface.
Definition at line 282 of file SessionManager.php.
References $request, MediaWiki\User\User\getName(), MediaWiki\User\User\saveSettings(), and MediaWiki\User\User\setToken().
◆ isUserSessionPrevented()
| MediaWiki\Session\SessionManager::isUserSessionPrevented | ( | $username | ) |
Test if a user is prevented.
- Access: internal
- For use from SessionBackend only
- Parameters
-
string $username
- Returns
- bool
Definition at line 530 of file SessionManager.php.
◆ logPotentialSessionLeakage()
| MediaWiki\Session\SessionManager::logPotentialSessionLeakage | ( | ?Session | $session = null | ) |
Write debug logs if the current request may have experienced session leak bug.
If the same session is suddenly used from a different IP, that's potentially due to a session leak bug, so log it for investigation. In most cases, these are false positives simply due to a user switching connections. Noisy logs are fine, because we only use this audit trail by looking up a specific username.
This also logs for unexpected changes to the "mwuser" cookie, an analytics cookie set from mediawiki.user.js, which should be a little less noisy.
- Access: internal
- For use in Setup.php only
- Parameters
-
Session | null $session For testing only
Definition at line 1086 of file SessionManager.php.
◆ preventSessionsForUser()
| MediaWiki\Session\SessionManager::preventSessionsForUser | ( | $username | ) |
Prevent future sessions for the user.
The intention is that the named account will never again be usable for normal login (i.e. there is no way to undo the prevention of access).
- Access: internal
- For use from \MediaWiki\User\User::newSystemUser only
- Parameters
-
string $username
Definition at line 515 of file SessionManager.php.
◆ setHookContainer()
| MediaWiki\Session\SessionManager::setHookContainer | ( | HookContainer | $hookContainer | ) |
- Access: internal
- Parameters
-
HookContainer $hookContainer
Definition at line 134 of file SessionManager.php.
◆ setLogger()
| MediaWiki\Session\SessionManager::setLogger | ( | LoggerInterface | $logger | ) |
Definition at line 126 of file SessionManager.php.
◆ shutdown()
| MediaWiki\Session\SessionManager::shutdown | ( | ) |
Save all active sessions on shutdown.
- Access: internal
- For use by Setup.php
Definition at line 583 of file SessionManager.php.
◆ validateJwtSubject()
| MediaWiki\Session\SessionManager::validateJwtSubject | ( | array | $jwtData, |
| UserIdentity | $user ) |
Partially validate JWT data that's presumed to be generated by getJwtData().
- Parameters
-
array $jwtData Claim data in the JWT (the full set, not just the subject). Callers should obtain it via JwtCodec, this method doesn't duplicate the checks there. UserIdentity $user Validation will only succeed if this user is the subject. Can be anonymous.
- Exceptions
-
JwtException on invalid data
- Since
- 1.45
- See also
- self::getJwtData()
- JwtCodec::parse()
Definition at line 439 of file SessionManager.php.
◆ validateSessionId()
|
static |
Validate a session ID.
- Parameters
-
string $id
- Returns
- bool
Definition at line 498 of file SessionManager.php.
Referenced by MediaWiki\Session\SessionInfo\__construct(), MediaWiki\Session\ImmutableSessionProviderWithCookie\getSessionIdFromCookie(), and MediaWiki\Session\CookieSessionProvider\provideSessionInfo().
The documentation for this class was generated from the following file:
- includes/Session/SessionManager.php
